Microsoft Defender XDR Deceptions Feature
Last year Microsoft announced a deception capability in Microsoft Defender for Endpoint. The idea with the deception is that adversaries access a Decoys or Lure which will trigger an incident for the response team to act on.
In Settings > Endpoints > Advanced features
Enable Deception

To create Deception rules
In Settings > Endpoints > Deception rules
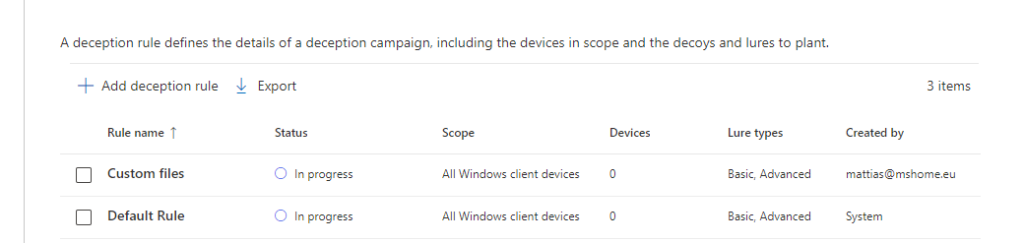

It is possible to scope this specific deception rule to Devices with a specific tag

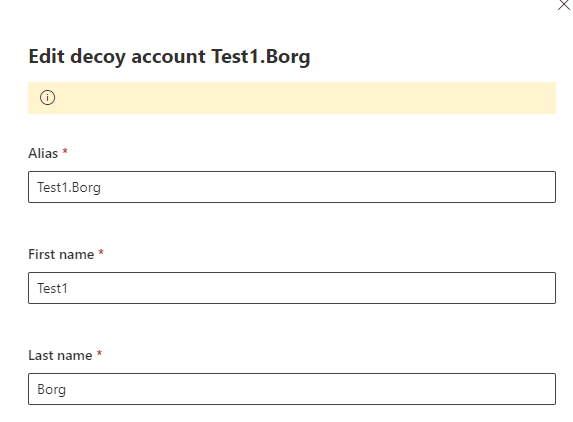
The system will automatically generate Alias or Hostnames which can be edited to better fit your organization
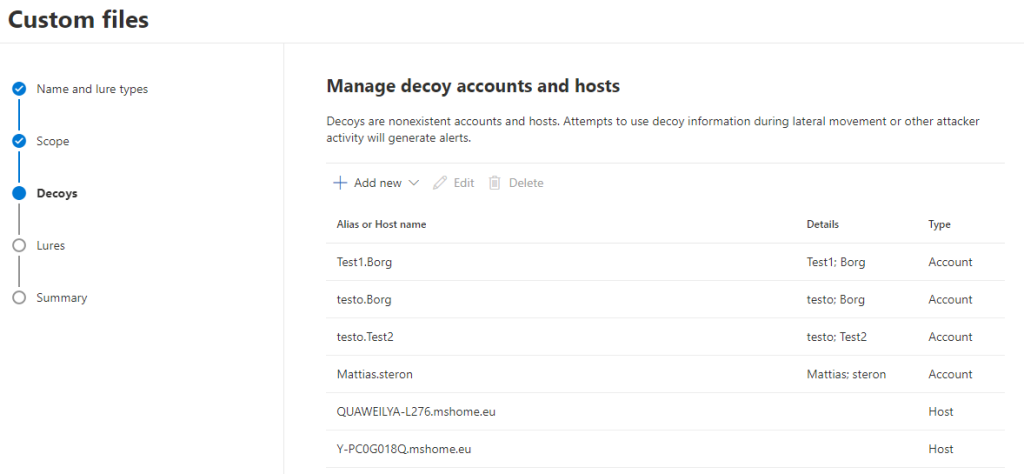
Lures can be autogenerated or use custom lures (file size up to 10MB)
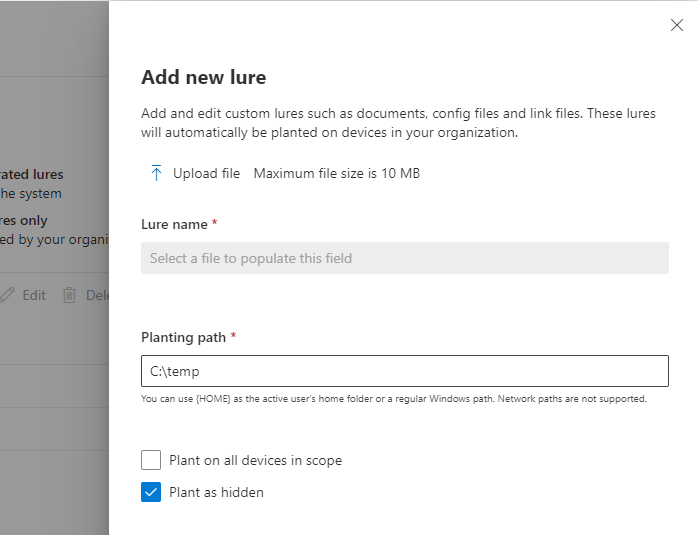
A Lure can be of any filetype except PE files (exe and dll)
It is recommended that the lure contains information of decoys.
Happy Hunting!