Security

DisruptionAndResponseEvents Table Preview

What can be more exciting than new Advance Hunting tables. Since it’s Preview it could change

The DisruptionAndResponseEvents table in Microsoft Defender XDR is your visibility layer into automatic attack disruption – Microsoft’s built-in capability to actively stop attacks in progress.

It records what Defender did, not just what the attacker did.

Telemetry

Most telemetry tells you what happened while this table tells you how an attack was disrupted in real time and it helps you understand attack scope, attack impact and Defender’s automated response decisions.

What kind of events you’ll see?

The table focuses on defensive actions

  • Containment actions
  • Examples:
  • User logon blocked
  • SMB access blocked
  • RPC access denied
  • RDP sessions disconnected

Hardening & protection policies

  • Safe Boot blocked
  • Safe Boot Guard applied
  • Group Policy hardening applied
  • SYSVOL access blocked

These indicate environment hardening triggered automatically

Session / activity termination

  • SMB session killed
  • Remote session logged off

These show active attacker sessions being cut off

Important nuance (most people miss this) the table does NOT log the action itself (like “Contain User”) instead, it logs the resulting effects, such as:

  • Blocked logons
  • Denied access
  • Policy enforcement

Data sources & dependencies

Populated from multiple Defender services (Endpoint, Identity, etc.) which requires proper onboarding – otherwise you’ll see little or no data

No onboarding = no visibility.

This table shines when you want to answer:

  • What did Defender automatically stop?
  • Why did this attack fail?
  • Which users/devices were actively contained?
  • What hardening actions were triggered during an incident?

If you want to have the table extended with the description you can use the following User-defined function (which runs in query time in Defender)

For further information about Attack Disruption, please visit: Automatic attack disruption in Microsoft Defender – Microsoft Defender XDR | Microsoft Learn

#Happy Hunting

Unified detections in Defender XDR

Something detection engineers (working with Defender XDR) has been waiting for is being able to use other static data to enrich queries. In Sentinel we have been able to use watchlists for a long time but on the Defender side this has been missing.

Some short updates (this give value):

_GetWatchlist('ExcludedIPs')

So what happens when you configure a new detection?

The detection wizard is showing and one of the new things here is the Frequenzy “Custom” which is familiar from a Sentinel perspective.

When it comes to lookback time, there are a few things to know:

https://learn.microsoft.com/en-us/defender-xdr/custom-detection-rules

In the next step, the Alert settings we have the opportunity to dynamically set the Provider name and other custom details (key value pairs)

We can also do detailed entity mapping as well as “Related Evidence” mapping. This means Entities that are related to the alert, but are not impacted assets.


Depending on data source we can also configure automated actions (as before).

We recommend you to AVOID doing isolate device as an automated action, things can go wrong fast.

Comparison between Analytics rules and custom detections: Compare Microsoft Sentinel analytics rules and Microsoft Defender custom detections – Microsoft Security | Microsoft Learn

#Happy Hunting


New security KQL functions focused around graph

Microsoft has published a set of new security functions (user-defined) in KQL. These are focused on the graph mindset, meaning relationships between nodes (objects). A previous blogpost explains graph semantics a bit more:

Graph semantics in Kusto – SEC-LABS R&D

The new functions released has many goodies, such as calculating blast radius, exposure perimeter and much more

User-defined functions can be saved as functions in Defender XDR or executed within the query itself.

Function NameDescription
detect_anomalous_new_entity_fl()Detect the appearance of anomalous new entities in timestamped data.
detect_anomalous_spike_fl()Detect the appearance of anomalous spikes in numeric variables in timestamped data.
graph_blast_radius_fl()Calculate the Blast Radius (list and score) of source nodes over path or edge data.
graph_exposure_perimeter_fl()Calculate the Exposure Perimeter (list and score) of target nodes over path or edge data.
graph_node_centrality_fl()Calculate various metrics of node centrality (such as degree and betweenness) over graph data (edge and nodes).
graph_path_discovery_fl()Discover valid paths between relevant endpoints (sources and targets) over graph data (edge and nodes).

https://learn.microsoft.com/en-us/kusto/functions-library/functions-library?view=azure-data-explorer#cybersecurity-functions

Example query (with defined table as input) from learn

let edges = datatable (SourceNodeName:string, EdgeName:string, EdgeType:string, TargetNodeName:string, Region:string)[						
    'vm-work-1',            'e1',           'can use',	            'webapp-prd', 	          'US',
    'vm-custom',        	'e2',           'can use',	            'webapp-prd', 	          'US',
    'webapp-prd',           'e3',           'can access',	        'vm-custom', 	          'US',
    'webapp-prd',       	'e4',           'can access',	        'test-machine', 	      'US',
    'vm-custom',        	'e5',           'can access',	        'server-0126', 	          'US',
    'vm-custom',        	'e6',	        'can access',	        'hub_router', 	          'US',
    'webapp-prd',       	'e7',	        'can access',	        'hub_router', 	          'US',
    'test-machine',       	'e8',	        'can access',	        'vm-custom',              'US',
    'test-machine',        	'e9',	        'can access',	        'hub_router', 	          'US',
    'hub_router',           'e10',	        'routes traffic to',	'remote_DT', 	          'US',
    'vm-work-1',            'e11',	        'can access',	        'storage_main_backup', 	  'US',
    'hub_router',           'e12',	        'routes traffic to',	'vm-work-2', 	          'US',
    'vm-work-2',        	'e13',          'can access',	        'backup_prc', 	          'US',
    'remote_DT',            'e14',	        'can access',	        'backup_prc', 	          'US',
    'backup_prc',           'e15',	        'moves data to',        'storage_main_backup', 	  'US',
    'backup_prc',           'e16',	        'moves data to',        'storage_DevBox', 	      'US',
    'device_A1',            'e17',	        'is connected to',      'sevice_B2', 	          'EU',
    'sevice_B2',            'e18',	        'is connected to',      'device_A1', 	          'EU'
];
let nodes = datatable (NodeName:string, NodeType:string, NodeEnvironment:string, Region:string) [
        'vm-work-1',                'Virtual Machine',      'Production',       'US',
        'vm-custom',                'Virtual Machine',      'Production',       'US',
        'webapp-prd',               'Application',          'None',             'US',
        'test-machine',             'Virtual Machine',      'Test',             'US',
        'hub_router',               'Traffic Router',       'None',             'US',
        'vm-work-2',                'Virtual Machine',      'Production',       'US',
        'remote_DT',                'Virtual Machine',      'Production',       'US',
        'backup_prc',               'Service',              'Production',       'US',
        'server-0126',              'Server',               'Production',       'US',
        'storage_main_backup',      'Cloud Storage',        'Production',       'US',
        'storage_DevBox',           'Cloud Storage',        'Test',             'US',
        'device_A1',                'Device',               'Backend',          'EU',
        'device_B2',                'Device',               'Backend',          'EU'
];
let nodesEnriched = (
    nodes
    | extend IsValidStart = (NodeType == 'Virtual Machine'),             IsValidEnd = (NodeType == 'Cloud Storage')              // option 1
    //| extend IsValidStart = (NodeName in('vm-work-1', 'vm-work-2')),     IsValidEnd = (NodeName in('storage_main_backup'))       // option 2
    //| extend IsValidStart = (NodeEnvironment == 'Test'),                 IsValidEnd = (NodeEnvironment == 'Production')          // option 3
);
let graph_path_discovery_fl = (   edgesTableName:string, nodesTableName:string, scopeColumnName:string
								, isValidPathStartColumnName:string, isValidPathEndColumnName:string
								, nodeIdColumnName:string, edgeIdColumnName:string, sourceIdColumnName:string, targetIdColumnName:string
								, minPathLength:long = 1, maxPathLength:long = 8, resultCountLimit:long = 100000) 
{
let edges = (
    table(edgesTableName)
    | extend sourceId           = column_ifexists(sourceIdColumnName, '')
    | extend targetId           = column_ifexists(targetIdColumnName, '')
    | extend edgeId             = column_ifexists(edgeIdColumnName, '')
    | extend scope              = column_ifexists(scopeColumnName, '')
    );
let nodes = (
    table(nodesTableName)
    | extend nodeId             = column_ifexists(nodeIdColumnName, '')
    | extend isValidPathStart   = column_ifexists(isValidPathStartColumnName, '')
    | extend isValidPathEnd     = column_ifexists(isValidPathEndColumnName, '')
    | extend scope              = column_ifexists(scopeColumnName, '')
);
let paths = (
    edges
    // Build graph object partitioned by scope, so that no connections are allowed between scopes.
    // In case no scopes are relevant, partitioning should be removed for better performance.
    | make-graph sourceId --> targetId with nodes on nodeId partitioned-by scope (
    // Look for existing paths between source nodes and target nodes with less than predefined number of hops
    // Current configurations looks for directed paths without any cycles; this can be changed if needed
      graph-match cycles = none (s)-[e*minPathLength..maxPathLength]->(t)
        // Filter only by paths with that connect valid endpoints
        where ((s.isValidPathStart) and (t.isValidPathEnd))
        project   sourceId                  = s.nodeId
                , isSourceValidPathStart    = s.isValidPathStart
                , targetId                  = t.nodeId
                , isTargetValidPathEnd      = t.isValidPathEnd
                , scope                     = s.scope
                , edgeIds                   = e.edgeId
                , edgeAllTargetIds          = e.targetId
    | limit resultCountLimit
    )
    | extend  pathLength                    = array_length(edgeIds)
            , pathId                        = hash_md5(strcat(sourceId, strcat(edgeIds), targetId))
            , pathAllNodeIds                = array_concat(pack_array(sourceId), edgeAllTargetIds)
    | project-away edgeAllTargetIds
    | mv-apply with_itemindex = SortIndex nodesInPath = pathAllNodeIds to typeof(string), edgesInPath = edgeIds to typeof(string) on (
        extend step = strcat(
              iff(isnotempty(nodesInPath), strcat('(', nodesInPath, ')'), '')
            , iff(isnotempty(edgesInPath), strcat('-[',  edgesInPath, ']->'), ''))
       | summarize fullPath = array_strcat(make_list(step), '')
    )
);
paths
};
graph_path_discovery_fl(edgesTableName          = 'edges'
                , nodesTableName                = 'nodesEnriched'
                , scopeColumnName               = 'Region'
                , nodeIdColumnName              = 'NodeName'
                , edgeIdColumnName              = 'EdgeName'
                , sourceIdColumnName            = 'SourceNodeName'
                , targetIdColumnName            = 'TargetNodeName'
                , isValidPathStartColumnName    = 'IsValidStart'
                , isValidPathEndColumnName      = 'IsValidEnd'
)

Happy Hunting!

Another reason to make sure Defender is configured correctly

Attack Disruption

  • It uses Defender XDR’s ability to correlate signals from many different sources into a single, high-confidence incident through insights from endpoints, identities, email and collaboration tools, and SaaS apps.
  • It identifies assets controlled by the attacker and used to spread the attack.
  • It automatically takes response actions across relevant Microsoft Defender products to contain the attack in real-time by containing and disabling affected assets.

Previous blog post on Attack Disruption Automatic Attack Disruption Explained – SEC-LABS R&D

With all the capabilities provided within Attack Disruption, it’s important that Defender XDR is configured correctly. For instance, if you have configured a gMSA account for the MDI actions, and it does not work properly, it will affect disruption negatively.

MDE Prereqs

  • Minimum Sense version for contain user:v10.8470
  • Auto IR:  Full – remediate threats automatically (recommended for full coverage, no automated response turns off automatic disruption for device group)
  • Endpoint discovery set to Standard (not basic)

In MDE the most common configuration improvements seen are:

  • Sample submission is not configured to send files automatically
  • Cloud block out level is not set to high
  • Cloud block timeout period is not set to 50s

more on MDE in this previous post 3 common Defender for Endpoint configuration errors

MDI Prereqs

  • Validate DC auditing
  • Validate permissions for Action Account or use LocalSystem
  • Validate no other systems interfere with attack disruption, such as systems for auto activating users

MDO Prereqs

  • Mailboxes are required to be hosted in Exchange Online.
  • The following mailbox events need to be audited by minimum:
    • MailItemsAccessed
    • UpdateInboxRules
    • MoveToDeletedItems
    • SoftDelete
    • HardDelete
    • Safelinks policy needs to be present.

MDA Prereqs

  • Microsoft Defender for Cloud Apps must be connected to Microsoft Office 365 through the connector
  • App Governance must be turned on

Happy Hunting!

Automatic Attack Disruption Explained

Some time ago, Microsoft announced and released Automatic Attack Disruption which is a feature within the Microsoft Defender XDR suite. Since then it has growth and from working for a service provider of Managed Detection and Response and running 100% Microsoft XDR, this is an amazing feature.

This blogpost will explain different aspects of disruption and how certain things works and the requirements in form of configurations to make it work.

Please note: All screenshots from Defender is from a Demo and Lab tenants and not customer tenants

Incident view attack disruption

The feature has to many parts possible to write a blog post about on its own, but let’s start somewhere:

Automatic Attack Disruption is not a new Auto IR (MDE) that acts on a single detection and tries to remediate according to defined playbook. Attack Disruption is chain of events, lower signals, such as RDP login to next event to next etc. until a certain level of confidence is reached. When the confidence reaches 99%+ SNR (Signal to Noise Ratio) then it kicks in. But it doesn’t simply stops processes or uses other classical Antimalware techniques, it goes back to the initial event and blocks everything used on the way.

Example scenario:

Internet to exposed RDP > Ask for service tickets for all SPNs (Kerberoast) > [Offline crack] > Login interactively to a server from the compromised RDP using one of the credentials from the Kerberoast attack > Enumerate ADCS templates > enroll certificate with new SAN > Domain admin

What Attack disruption will do is take a note of the initial RDP (similar to a human like: “Ok, someone used RDP, it’s not malicious but I will keep an eye on it”).

Next step is the Kerberoast

Still not malicious activities depending on how the threat actor executes that it could be an SPN enumeration alert. However, asking DC for a ticket is how Active Directory works and let’s play this as no incidents are generated in this case.

Threat Actor’s next step, after the tickets where cracked and the SPN account password is now in clear text (using hashcat, john to crack the password). Now it’s time for Threat Actor to login using these credentials and they user RDP to login interactively on the remote server.

The server they end up on has access as system to enroll a vulnerable certificate template (ESC1) and becomes domain admin using a sensitive account as the SAN name.

When Attack Disruption is over 99% certain that this is malicious activities, it kicks in. Remember that just RDP is very common still by both users and admins and Attack Disruption does not kick in until it is certain.

What is awesome with the feature is that when it kicks in, it takes care of entities involved in the chain, to completely block the Threat Actor. Such as containing device (If not onboarded to MDE, it will tell all onboarded endpoints that they are not allowed to communicate with the mentioned device). The involved users will be contained as well, blocking them from logons and disabling accounts.

Another example I would like to explain is the Business Email Compromise, BEC

A user clicks on a phishing link (even if we, as a community pushes security awareness, it still happens frequently)

The user who clicked ends up on the link lands on a phishing website, which act as a proxy and therefor can handle MFA requests as well since the proxy will try authenticate to, in this case, Office 365

MFA

From the Threat Actor side and the Evilginx, the authentication is captured

The cookies from the authentication can then be injected to the browser and the threat actors are logged in.

The Threat Actor then takes further steps, such as configure rules to exfiltrate all incoming emails using a forward rule to an external email address, or send a email to finance department to pay an invoice, and configure a rule to move all replies to such email to another folder to avoid the compromised user to notice this.

Back to Attack Disruption…

So what happens in the last scenario is that the service detects the events which by themselves might not be that bad, but when chained it’s certain that it’s something bad going on and disruption kicks in to stop the attack.

Another example

Attack Disruption is definitely a game-changer. When it detects something bad it will take actions on all assets used by the Threat actor automatically which will happen faster than a human can react and click. The humans are still needed, but this is a great feature the back the human SecOps.

Building Disruption Scenarios

When Microsoft develop new scenarios, they start, as in proactive Threat Hunting, with a hypothesis.

  • Research creates hypothesis
  • Research validates hypothesis in telemetry
  • Detector(s) development for events worth noticing
  • Detectors trigger as non-customer facing detections
    (establish 99% confidence)
  • Non customer facing alerts are manually investigated
    (establishing 99%  confidence)
  • Release alerts to customers
    (not taking action)
  • Alerts are released but throttled – Disrupt engages
    (Triggered alerts are manually investigated)
  • Alerts are released through release rings
    (Customer grading is monitored)
  • Customers with Disrupt incidents are being contacted and interviewed
    (Validating response efficacy)
  • Scenario gets released to all customers
  • Detector are being reviewed and updated
    (based on new TTPs and customer feedback/ researcher grading)

From correlated signals to disruption

Scenarios and requirements

EndpointsOn-Prem IdentityOffice 365Cloud AppsSentinelCloud Identity
Human Operated Ransomware****
Hands on Keyboard Attack**
Business Email Compromise****
Adversary-in-the-Middle**********
Compomised Credentials by
Known Threat Actor
****
Credential Stuffing****
Compromised IaaS Cloud Resource**
SAP Financial Process Manipulation
(3rd Party Signals required)
****

Attack Simulation Training to be resilient against QR code phishing

QR code has been a hassle in the cyber world since a while back. There are multiple reasons for threat actors to use this method to phish uses and compromise accounts.

One reason is that it is difficult to detect (the MDO research team has done a great job in detecting these, huge kudos to you!) the other reason is that we force the user to move to another device. If they read the email on their monitored laptop, and then scan the QR with the phone it is more difficult to detect, and not all organizations have onboarded their phone to Defender.

Microsoft announced last month about partnership with Fortra’s Terranova Security and have launched two new QR code phishing training modules available in Attack Simulation Training. THis will provide a training email for the end-user which explains the QR code technique

How to launch a simulation with QR code

Go to Defender XDR portal and in the Email & Collaboration you select Attack simulation training

Select Launch a simulation and follow the wizard

Select the How-to Guide

Select payload Teching Guide: How to recognize and report QR phishing messages

Choose your targets

If required, exclude users

Configure your launch details

Monitor

Don’t forget to follow up your simulations with user awareness training to establish a cyber security culture

Happy Hunting!

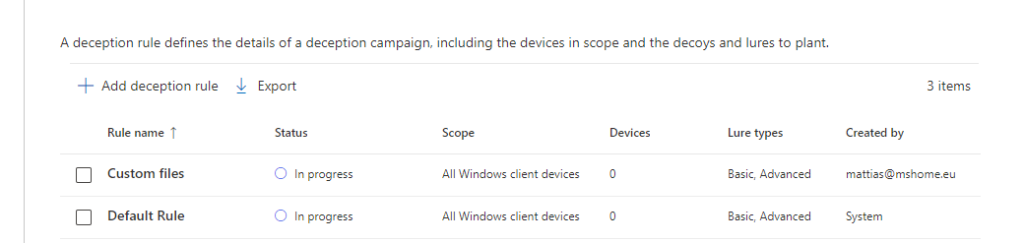
Microsoft Defender XDR Deceptions Feature

Last year Microsoft announced a deception capability in Microsoft Defender for Endpoint. The idea with the deception is that adversaries access a Decoys or Lure which will trigger an incident for the response team to act on.

In Settings > Endpoints > Advanced features

Enable Deception

To create Deception rules

In Settings > Endpoints > Deception rules

It is possible to scope this specific deception rule to Devices with a specific tag

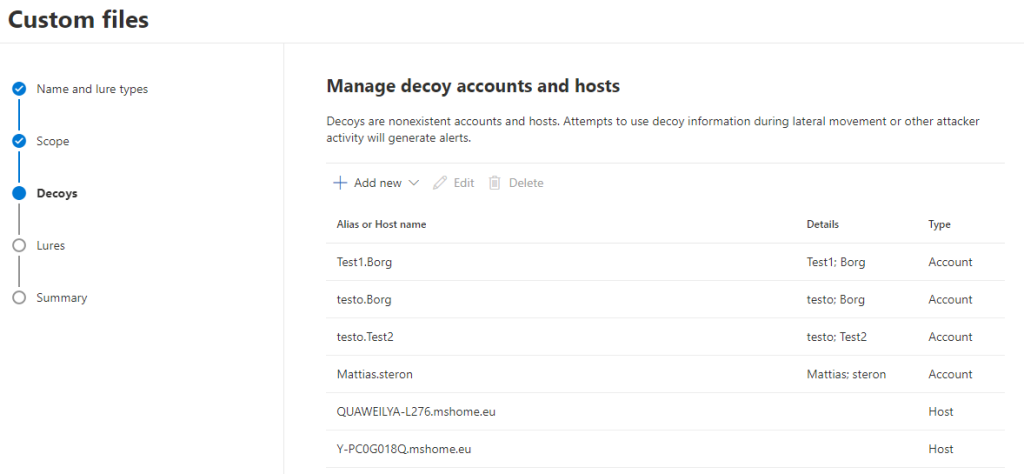
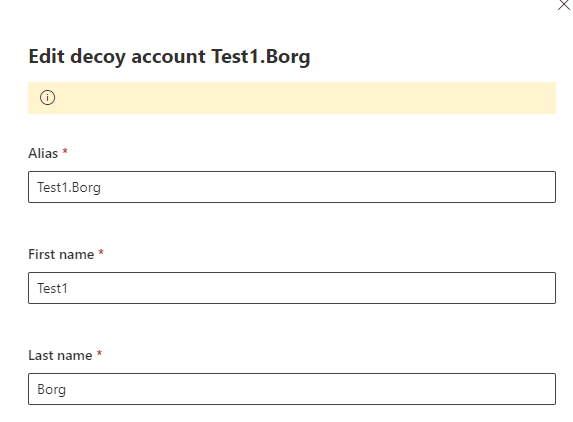
The system will automatically generate Alias or Hostnames which can be edited to better fit your organization

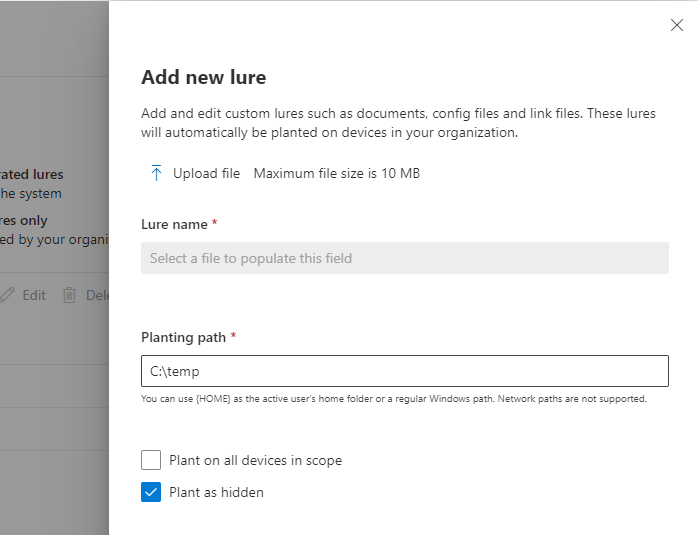
Lures can be autogenerated or use custom lures (file size up to 10MB)

A Lure can be of any filetype except PE files (exe and dll)
It is recommended that the lure contains information of decoys.

Happy Hunting!

QR Code phishing and MDO

QR code phishing campaigns have most recently become the fastest growing type of email-based attack. These types of attacks are growing and embed QR code images linked to malicious content directly into the email body, to evade detection. They often entice unwitting users with seemingly genuine prompts, like a password reset or a two-factor authentication request. Microsoft Defender for Office 365 is continuously adapting as threat actors evolve their methodologies. In this blog post we’ll share more details on how we’re helping defenders address this threat and keeping end-users safe.

It’s Friday and blog time

It’s difficult to detect for security vendors due to low signal for ML detection due to basically no text, embedded in attachments and so on. It’s brilliant as an attack technique.

MDO and EOP detects QR code inline in the mail flow and analyze the metadata and send the URL behind the QR to sandbox

All other attributes are also used for the final email verdict.

Statistics Microsoft Defender for office and QR code phishing at scale

  • With the power of existing capabilities and robust tools we have built, many heuristics-based rules were released within minutes leading to ~1.5 million QR code phishing blocked in email body per day in the last several months! As the attack patterns evolve, new rules continue to get released and refined as needed.
  • The advanced detection technologies built to extract QR code related metadata (URL and text), have scanned more than 200 million unique URLs on average weekly, out of which more than 100 million came from QR codes.
  • Our advanced detection technologies have blocked more than 18 million unique phishing emails containing a QR code image in the email body on average weekly and around 3 million unique QR code phishing emails per day.
  • QR code phishing protection includes Commercial as well as Consumer emails. More than 96% of these are QR code phishing blocked by our technologies in Enterprise alone.

From: Protect your organizations against QR code phishing with Defender for Office 365 – Microsoft Community Hub

But even if you have all great security in-place, we can still not patch the end-users. User awareness training is critical for your data

We recommend you to read the full post at Protect your organizations against QR code phishing with Defender for Office 365 – Microsoft Community Hub

Happy Hunting

Quick tip – Country Codes

All countries has an ISO code, described in ISO 3166 is an international standard.
These codes are used throughout the IT industry by computer systems and software to make it easier to identify a country.

It has multiple formats and they country codes are presented in the following formats: Alpha-2 (2 characters), Alpha-3 (3 characters) and Numeric (3 digits).

In the data from some logs like SigninLogs and IdentityLogonEvents the country is presented as Alpha-2. We realized pretty quick is that some 2-characters country codes are difficult to remember. As in below, picture it could be difficult to know all these countries.

We have been using this for a long time and thought it might be something others can use as well.

So to solve this I created a csv file and placed on github:

https://raw.githubusercontent.com/mattiasborg82/Hunting/main/General/cc.txt

To be able to join our data with this file we can use the external data operator in Kusto

Since it’s a CSV file, we can make it more usable by split the rows on comma

To to build the full use-case for this, we join it with our SigninLogs (or other logs that uses the country code)

Copy friendly code

let CountryCodes = externaldata (CountryCode:string)
[
 @"https://raw.githubusercontent.com/mattiasborg82/Hunting/main/General/cc.txt"
]
with(ignoreFirstRecord=true);
SigninLogs
| where isnotempty(Location)
| join kind=leftouter (
    CountryCodes
    | extend Country = tostring(split(CountryCode, ",")[0]),
              Location = tostring(split(CountryCode, ",")[1])
    | project-away CountryCode)
on Location
| summarize count() by Country,UserDisplayName

This can be used further to combine with conditional access blocks showing potential credential leak

Happy Hunting!

Threat Hunting and the New Hunts in Sentinel
Establishing a Proactive Hunting program is something which is useful and necessary today.
From working with proactive threat hunting for a long time, from when data was not available at your fingertips, things has become a lot easier in the era of SIEM and over the last years, EDR and XDR.
The technical part is the easy one. The process of establishing your hunting and connect it with existing processes is usually what’s difficult.

What is proactive Hunting?

First, what is threat hunting?

To dive in to this topic I want to point out activities that are somewhat related

The custom detections or scheduled rules is pretty clear what it is. but Tasks is something which sits in between Proactive Threat Hunting and Custom Detections.
Tasks are things discovered in Hunting, and data of interest but cannot be set as a custom detection as of yet.

The reasons could be many, but for example to noisy data and no good correlation values or near-time events that can be used to reduce False-Positives. Even though we have finalized our hypothesis from threat hunting we might want to follow-up on the events, maybe on a daily basis, but we cant have it scheduled since it will give an incident fatigue.

To summarize tasks, it’s queries that might make it to a detection but for now we run it automatically or manual and do manual review on the result on a daily schedule.

To iterate back to threat hunting before we take a look at the hunts feature in Sentinel

Threat Hunting can be divided into 2 main pillars; Proactive and Reactive hunting

Proactive Threat Hunting is when you don’t know something is going on, like playing hide-n-seek, except for that you don’t know anyone is playing with you

Reactive Threat Hunting is post breach/post incident and you use threat hunting to find the outer boundaries of the incident, which could be other devices communicating with a specific IP, list all process communicating, find the same processes on other devices, and then which IP’s they are communicating with.

In the EDR era or now, the XDR era, threat hunting becomes easier on a technical level. The data collection happens automatically for many workloads and not only collected, it’s streamed.

With the power of Kusto Query Language, you can do advanced aggregations, anomaly calculations and visualizations to truly crunch and bend your data.

In Proactive Threat hunting, you will start your assignment by defining your Hypothesis, which could be something like “I would like to see if any local users have been added outside the process”

Then you check what ever data you need to discover such activities (DeviceEvents/DeviceProcessEvents hint hint) and you continue to develop the query for is and document your result.

Here is what makes Hunts feature so great. It actually allows for process integration, like we have in Microsoft 365 Defender where we can create incidents based on the results and have it handled by the incident process.

Hunts in Sentinel

Common use cases:

  • Proactively hunt based on specific MITRE techniques, potentially malicious activity, recent threats, or your own custom hypothesis.
  • Use security-researcher-generated hunting queries or custom hunting queries to investigate malicious behavior.
  • Conduct your hunts using multiple persisted-query tabs that enable you to keep context over time.
  • Collect evidence, investigate UEBA sources, and annotate your findings using hunt specific bookmarks.
  • Collaborate and document your findings with comments.
  • Act on results by creating new analytic rules, new incidents, new threat indicators, and running playbooks.
  • Keep track of your new, active, and closed hunts in one place.
  • View metrics based on validated hypotheses and tangible results.

In Sentinel go to Hunting and Hunts

Here is the list of previous hunts.

If you select New Hunt we can create a new

You can add the Hypothesis and choose if it’s Validated or not (which can be set later in the process by another Threat hunter)

When we have our new Hunting campaign, we can add queries

Adding Tactics and techniques and map entities

It’s possible to create incidents from the results to map to the incident process, and we can also start automated playbooks (entity-based) from the entity pane.

Summary

There are so many details on this feature and it has some many capabilities. The best part is that it has the process of hunting as its core. Now it’s easier to deliver threat hunting, as a service, as a consultant or if you work internally for an organization.

Happy Hunting